Security & Compliance
We engineer secure software platforms. This document details our DevSecOps practices, encryption standards, secure coding lifecycles, and compliance readiness parameters.
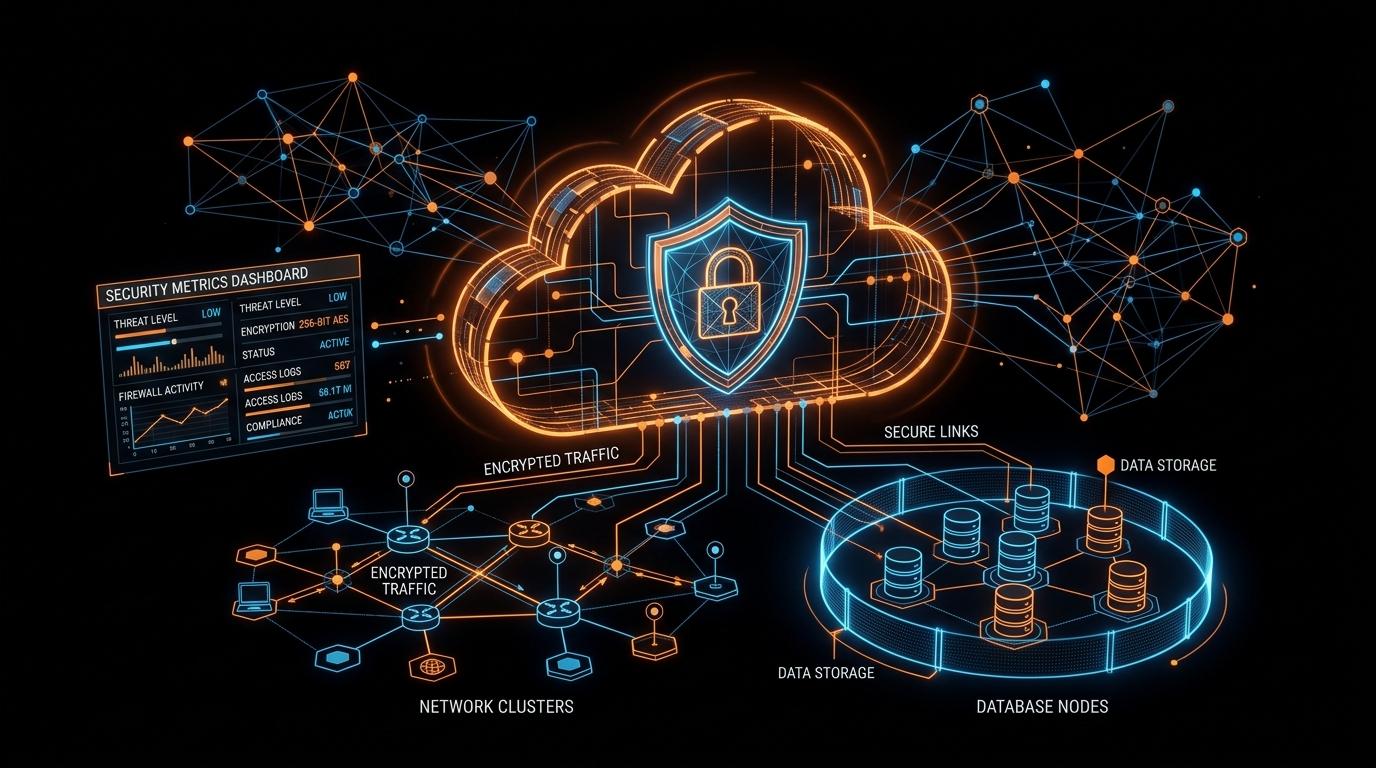
Table of Contents
- 1. Secure SDLC & Code Reviews
- 2. OWASP Compliance
- 3. DevSecOps & CI/CD Pipelines
- 4. Encryption Standards
- 5. Role-Based Access Control
- 6. Infrastructure & Cloud Security
- 7. Continuous Monitoring
- 8. Backups & Disaster Recovery
- 9. Incident Response Lifecycle
- 10. Responsible Disclosure Policy
- 11. Compliance Readiness Statement
1. Secure SDLC & Code Reviews
We integrate security directly into our Software Development Lifecycle (SDLC). Our engineering squads implement mandatory, multi-developer code reviews for all codebase commits. Static Application Security Testing (SAST) tools automatically scan commits for hardcoded secrets, injection flaws, and package vulnerabilities prior to merge.
2. OWASP Compliance
Our backend and web application engineers code in compliance with the Open Web Application Security Project (OWASP) Top 10 guidelines. We enforce strict protocols regarding input validation, parameterized SQL queries, secure cross-site scripting (XSS) filters, and context-aware escaping to eliminate web exploit boundaries.
3. DevSecOps & CI/CD Pipelines
We operationalize DevSecOps by automating vulnerability scans within our CI/CD pipelines (via GitHub Actions, GitLab CI, or Jenkins). Dependency analysis tools scan software manifests on every release, flagging outdated packages or licensing conflicts before staging deployments occur.
4. Encryption Standards
We enforce robust encryption layers across all deployed client environments:
- In Transit: All HTTP traffic is protected using Transport Layer Security (TLS 1.3/1.2) with strict HSTS directives.
- At Rest: Databases, logs, and storage buckets are encrypted using Advanced Encryption Standard (AES-256) with secure cloud key management systems (KMS).
5. Role-Based Access Control
We implement the principle of least privilege. Engineers are granted staging and repository access tokens strictly on a need-to-know basis, validated via Multi-Factor Authentication (MFA) and Single Sign-On (SSO) integrations.
6. Infrastructure & Cloud Security
All cloud network structures (built on AWS, Google Cloud, or Azure) are configured using Infrastructure as Code (IaC) templates, guaranteeing repeatable, hardened setups. We partition environments using Virtual Private Clouds (VPCs), strict security groups, and cloud IAM boundary configurations.
7. Continuous Monitoring
We monitor deployed services using centralized logging infrastructure (such as Prometheus, Grafana, CloudWatch, or Datadog). Anomalous request counts, authentication failures, and system metric spikes trigger high-priority alerts to on-call engineering teams.
8. Backups & Disaster Recovery
We configure daily, incremental system backups across isolated geographic availability zones. Backup files are encrypted, write-protected, and tested periodically via automated recovery drills to verify data integrity parameters.
9. Incident Response Lifecycle
TechWhizz maintains a documented security incident response protocol. In the event of a suspected security boundary breach, our dedicated response team initiates isolation procedures, logs telemetry data, conducts root-cause analysis, and complies with client notification directives within contract SLAs.
10. Responsible Disclosure Policy
We welcome security reports from independent researchers. If you identify a potential security vulnerability in our public web properties or open libraries, please report it privately to info@techwhizz.co. We request that you provide descriptive steps and refrain from disclosing the exploit publicly until we patch the boundary.
11. Compliance Readiness Statement
Please Note: TechWhizz operates as an engineering partner, developing solutions designed to meet strict regulatory guidelines (such as HIPAA for healthcare systems or GDPR for personal data protection). Actual regulatory compliance and audit certifications (such as SOC 2 Type II, ISO 27001, or HIPAA compliance) depend on client-side requirements, infrastructure hosting environments, and the final scope of the Statement of Work (SOW). TechWhizz does not hold corporate SOC 2 certificates directly but builds compliance-ready systems hosted on certified infrastructures.